Why PDPL compliance is non-negotiable for AI in Saudi Arabia
Saudi Arabia's Personal Data Protection Law (PDPL) is not just a compliance box to tick — it's a strategic enabler for enterprises that want to adopt AI responsibly. As AI agents become more autonomous, handling everything from procurement quotes to customer queries, the risk of non-compliance grows. PDPL mandates that personal data be processed lawfully, transparently, and with clear purpose. For decision-makers at Saudi enterprises, this means AI systems must be designed with data governance at their core, not as an afterthought.
Vision 2030's push for digital transformation makes this even more urgent. As Saudi organizations digitize operations, they collect more data — and more personal data. AI agents that act on this data must respect PDPL's principles: data minimization, purpose limitation, storage limitation, and individual rights. Failure to comply can result in significant fines and reputational damage, but more importantly, it erodes the trust that underpins successful AI adoption.
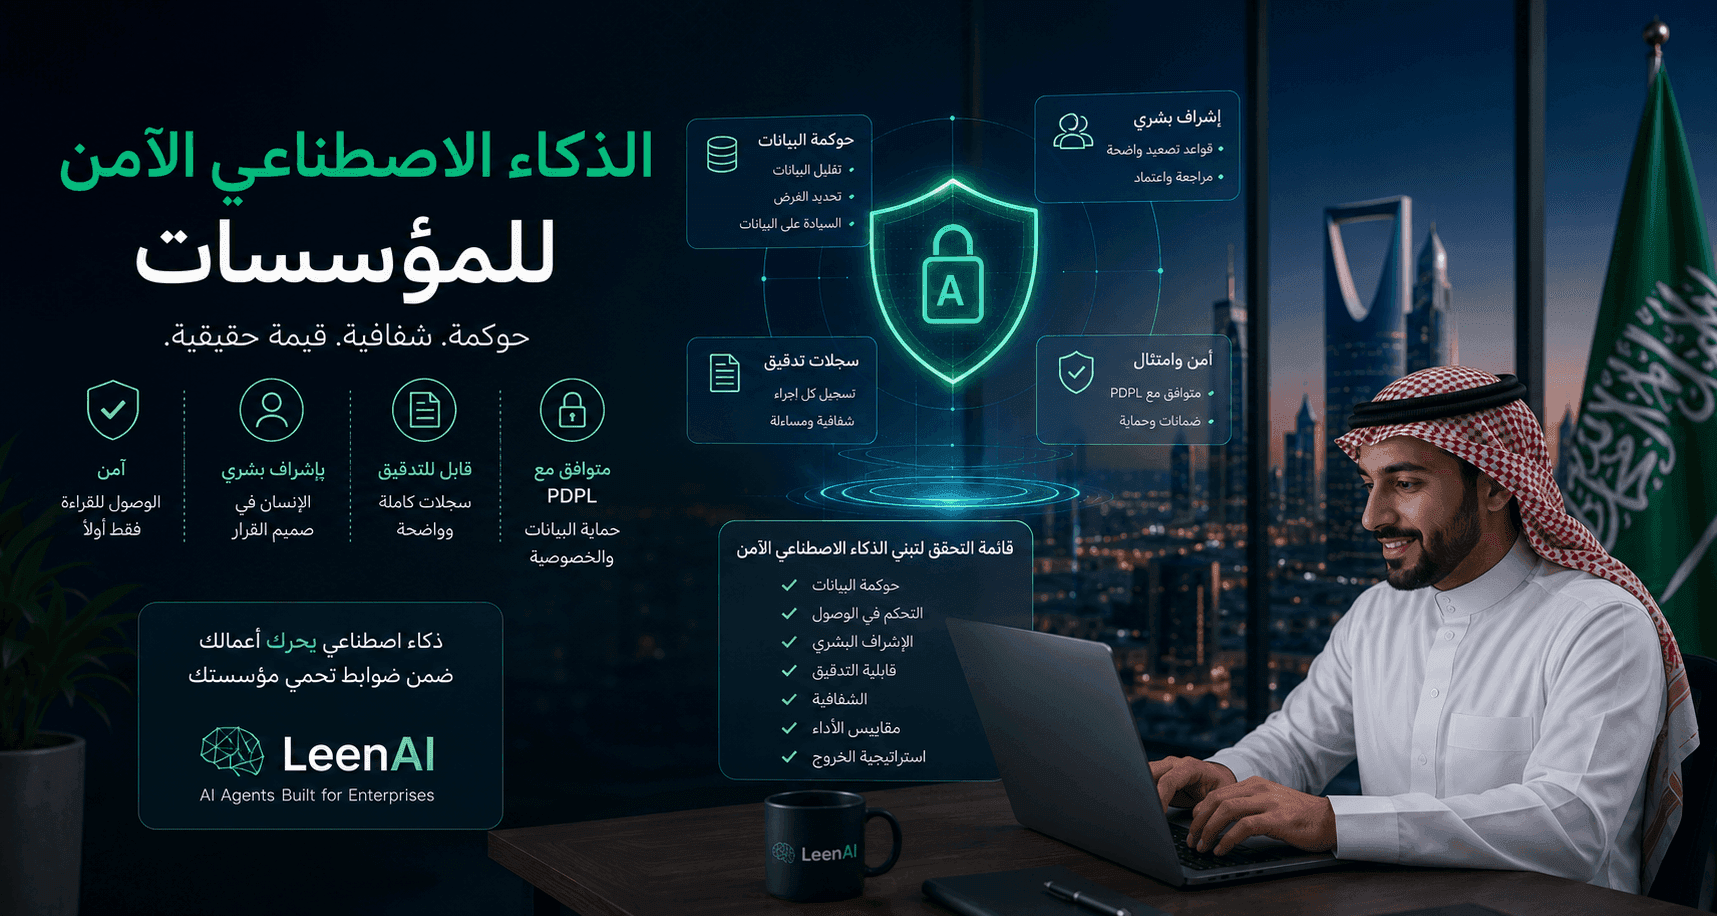
The good news? PDPL compliance and effective AI are not at odds. With the right architecture — read-only-first access, human-in-the-loop approvals, and audit logging — you can build AI agents that are both powerful and compliant. This checklist provides a practical path forward.
What does PDPL require from AI systems?
PDPL applies to any processing of personal data of individuals in Saudi Arabia, regardless of where the processing occurs. For AI systems, this means every stage — from data collection and training to inference and decision-making — must comply. Key requirements include:
- Lawful basis: You must have a legitimate reason to process personal data, such as consent or contract necessity.
- Purpose limitation: Data can only be used for the specific purpose it was collected for.
- Data minimization: Collect only the data you need; don't hoard data 'just in case'.
- Storage limitation: Keep data only as long as necessary.
- Individual rights: Allow individuals to access, correct, or delete their data.
- Security: Implement appropriate technical and organizational measures to protect data.
AI agents add complexity because they may make decisions or take actions based on personal data. For example, a customer service agent might access a customer's order history to resolve an issue. Under PDPL, you need to ensure that access is justified, limited to what's needed, and logged.
How do you ensure data minimization in AI agents?
Data minimization is a core PDPL principle, but it's often challenging with AI, which thrives on large datasets. The solution lies in the architecture of your AI agents. Instead of giving an agent unrestricted access to all data, design it with a read-only-first approach: the agent can read data it needs for a task, but it cannot modify or export data without explicit human approval.
For example, LeenAI's OpsRAG agent connects to your knowledge bases and documents, but it operates on a need-to-know basis. It retrieves only the information required to answer a query, and it never stores personal data beyond the session. This minimizes exposure and aligns with PDPL's data minimization requirement.
Another tactic is to use data masking or pseudonymization where possible. If an AI agent needs to process data for analytics, it can work with anonymized datasets. This reduces the risk of a breach and simplifies compliance.
Finally, implement retention policies that automatically delete or archive data after a specified period. This ensures you don't keep personal data longer than necessary, which is both a PDPL requirement and a best practice for reducing liability.
What role does human-in-the-loop play in PDPL compliance?
Human-in-the-loop is not just a nice-to-have; it's a key governance mechanism that helps ensure AI actions are appropriate and lawful. When an AI agent proposes an action that involves personal data — such as sending a personalized offer or updating a customer record — a human should review and approve it before it's executed.
This approach has several benefits:
- Accountability: Humans are ultimately responsible for decisions, aligning with PDPL's accountability principle.
- Error prevention: Humans can catch mistakes or biases that AI might miss.
- Auditability: Every human approval is logged, creating a clear trail of who authorized what.
For instance, in a procurement scenario, an AI agent like SmartQuote can generate a quote based on customer data, but a human must approve it before it's sent. This ensures that the quote is accurate and that the data used was appropriate.
LeenAI's AI agents are designed with human-in-the-loop by default. They can act autonomously on low-risk tasks, but for any action that involves personal data or significant business impact, they escalate to a human. This balances efficiency with compliance.
How do you maintain audit logs for AI actions?
Audit logs are essential for demonstrating compliance with PDPL. They provide a record of what data was accessed, when, by whom (or what system), and for what purpose. For AI agents, this means logging every action the agent takes, including:
- The input data it received.
- The output it generated.
- The decision path it followed.
- Any human approvals or overrides.
These logs serve multiple purposes: they help you detect unauthorized access, they support investigations in case of a breach, and they provide evidence of compliance during audits or regulatory inquiries.
To make audit logs effective, they must be tamper-proof and retained for an appropriate period. Consider using immutable storage or cryptographic hashing to ensure logs cannot be altered. Also, define who has access to logs and how long they are kept, aligning with PDPL's retention requirements.
LeenAI's agents come with built-in audit logging. Every action is recorded, and you can export logs for your compliance team or regulator if needed. This gives you full visibility into how your AI agents handle personal data.
What are the key steps to a PDPL-compliant AI pilot?
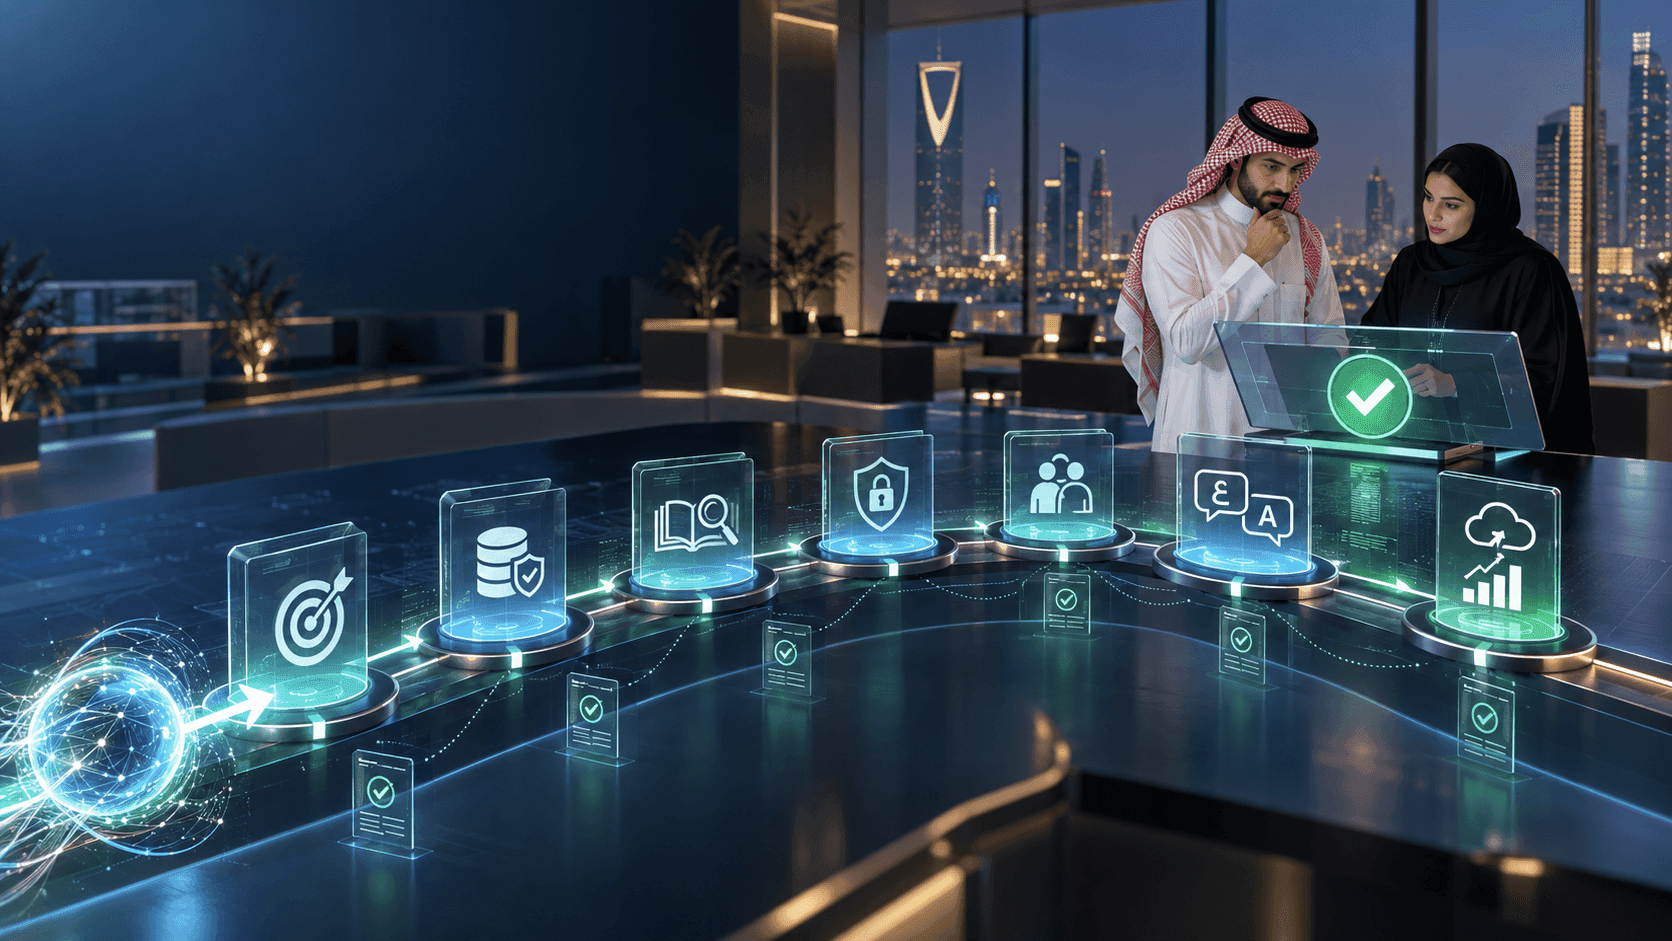
Running a pilot is a smart way to test AI in a controlled environment while ensuring compliance. Here's a step-by-step checklist for a PDPL-compliant AI pilot:
- Data mapping: Identify what personal data your AI agent will access and process. Document the data flows and the legal basis for processing.
- Consent and notices: If you're relying on consent, ensure you have a mechanism to obtain and record it. Provide clear privacy notices to individuals.
- Access controls: Implement role-based access so only authorized personnel and AI agents can access sensitive data.
- Read-only-first: Configure the AI agent to have read-only access to data, with write actions requiring human approval.
- Human-in-the-loop: Define which actions require human review and set up the workflow for approvals.
- Audit logging: Enable comprehensive logging from day one, and test that logs are being captured correctly.
- Data retention: Set up automatic deletion or archiving of data after the pilot ends or after a defined period.
- Vendor assessment: If you're using a third-party AI solution, assess its compliance with PDPL. Ensure it has appropriate safeguards.
- Training: Train your team on PDPL requirements and the AI system's governance features.
- Acceptance criteria: Define clear KPIs and acceptance criteria for the pilot, including compliance metrics.
LeenAI's Acceptance Pack covers all these elements. We provide UAT scripts, evaluation frameworks, runbooks, and training to help you launch a compliant pilot in weeks, not months.
How can LeenAI help you achieve PDPL compliance with AI?
LeenAI builds governed AI agents for Saudi enterprises, designed from the ground up to be PDPL-aware. Our agents — SmartQuote, WhatsApp CX, OpsRAG, and MAE — operate with read-only-first access, human-in-the-loop approvals, and full audit logging. They are bilingual (Arabic/English) and respect data residency requirements, keeping your data within Saudi Arabia.
We don't just deliver a slide deck; we deliver working AI that meets agreed KPIs. Every pilot comes with our Acceptance Pack, including UAT, evaluations, runbooks, and training, so you can prove compliance and value before scaling.
If you're ready to explore how governed AI can transform your operations while staying PDPL-compliant, talk to us or see how we scope pilots. For a deeper look at our agents, check out LeenAI's OpsRAG and SmartQuote.